
Severity
High
Analysis Summary
The South Asian cyber espionage group Bitter (also known as APT-C-08, APT-Q-37, Hazy Tiger, Orange Yali, T-APT-17, and TA397) has been observed targeting South Asian organizations using a previously undocumented Remote Access Trojan (RAT) named PapRAT. According to research, the malware has both C++ and Rust implementations, enabling attackers to execute commands, upload and download files, delete files, enumerate directories and drives, and capture screenshots. The Rust variant also supports PowerShell execution and additional commands.
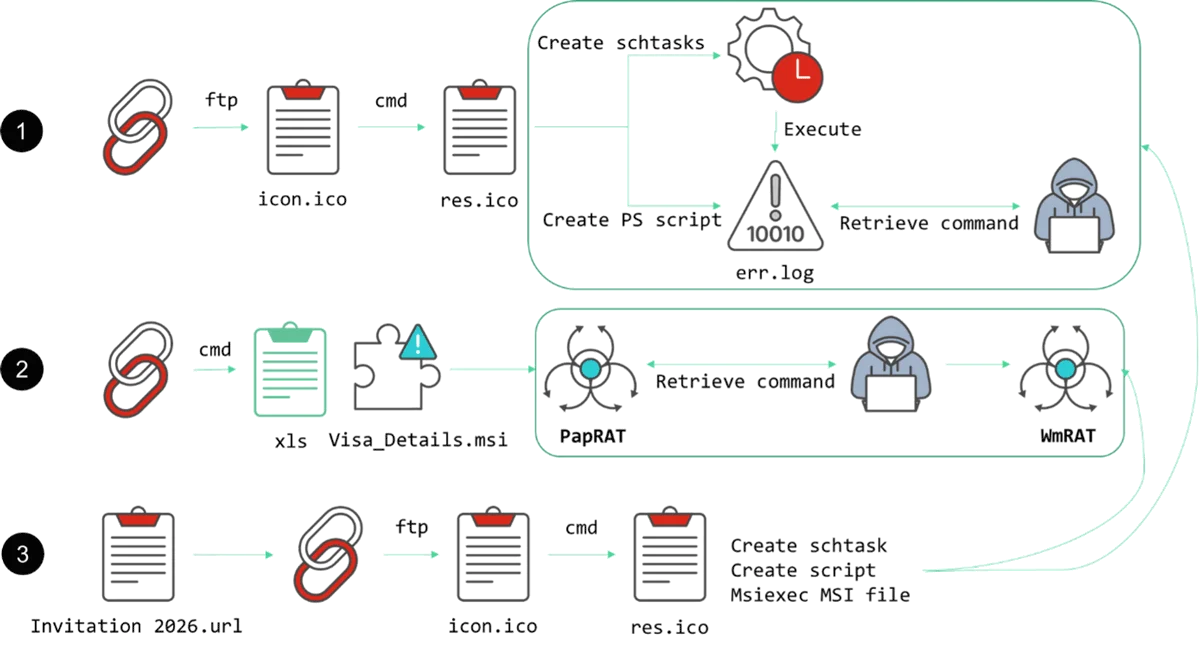
The campaign employs three different infection chains to deliver PapRAT. The first uses a malicious Windows Shortcut (LNK) file that abuses the legitimate ftp.exe utility to execute scripts and create scheduled tasks for persistent communication with a Command-and-Control (C2) server. The second involves a Virtual Hard Disk (VHDX) image containing an LNK file that opens a decoy Excel spreadsheet while silently executing an MSI installer to deploy PapRAT. The third uses a URL shortcut to retrieve an LNK file through WebDAV, which subsequently launches an MSI installer.
The attackers also employ Living-off-the-Land (LotL) techniques to execute remotely supplied commands and gather system reconnaissance, including directory listings, user folders, installed antivirus products, scheduled tasks, and mounted drives. Collected information is saved as abc.pdf and exfiltrated to attacker-controlled infrastructure using curl before being deleted from the compromised system. Another script retrieves talk.log, which contains Base64-encoded PowerShell instructions for executing additional commands.
PapRAT supports eight primary commands, including remote shell access, file management, arbitrary file execution, drive enumeration, and screenshot capture. Its Rust variant introduces three additional commands for PowerShell execution, sleep and polling operations, and process termination.
Furthermore, the third infection chain deploys WmRAT, another malware previously associated with Bitter. These developments demonstrate the group's evolving capabilities and continued efforts to maintain access to targeted systems. Organizations should monitor suspicious scripting activity, scheduled task creation, and unexpected LNK, URL shortcut, VHDX, and MSI files.
Impact
- Sensitive Information Theft
- Data Exfiltration
- Lateral Movement
- Operational Disruption
Indicators of Compromise
Domain Name
netmansrvdns.com
rappellingaart.com
MD5
1c54c50c1dafcd2d63e29d40251f0838
cfa759fca3efb8a794205809cdda8716
34115e4587dc5fb310f11c97b96a5300
8d335ec4439fc2a210092a00f16629fc
SHA-256
a3081df333ca7f18bd90d10a45125ab5011dcf9d2806feae2935f09cab07da4c
e3992f8c945b0761242377cba32d91b0a390c7cecd79478439843d93e6d2b76b
ccefbdec2718d864d9d33c743aabfcef88a8d7904d1c598bfcf15cf5f3591c88
569a21b519aaac8c92f653d708ab6ef34e3f38ea967f47e041d1e2425f6a4b33
SHA1
71c8351a8d63a2fb8589d1f4f3f8aedf73853fee
a31d30fd6d5ba22a148bbf7d9a120a9bbe8108a2
630f21883a6ba72d7adc13a7cb8344a8d60bcd8a
a3f1841ac4fb4f93c87bf74abb0718a9e1696c82
URL
- https://techtalkhelp.com/talk.log
- http://www.rivingtonclarks.com/beautiQuewonders/banaNa.php
- https://goodnfortunes.com/ucl.php
- https://felixfuturenext.com/Epistemological/
- http://gomescareerplans.com/docs
Remediation
- Block known malicious domains and IP addresses associated with PapRAT's command-and-control infrastructure.
- Restrict the execution of unauthorized LNK and URL shortcut files received through emails or external sources.
- Monitor suspicious use of legitimate utilities such as ftp.exe, curl, and PowerShell.
- Disable or restrict unnecessary WebDAV functionality to prevent malicious file retrieval.
- Implement application allowlisting to prevent unauthorized MSI installers and executables from running.
- Monitor scheduled task creation and modification to detect suspicious persistence mechanisms.
- Deploy and maintain updated endpoint detection and response (EDR) solutions to identify malicious activities.
- Inspect VHDX disk images and MSI packages before allowing them to execute.
- Restrict PowerShell execution through appropriate execution policies and application controls.
- Monitor unusual outbound network connections and data transfers to identify potential exfiltration.
- Apply network segmentation to limit unauthorized access and lateral movement.
- Keep operating systems, security tools, and applications updated with the latest security patches.
- Conduct regular threat hunting to identify PapRAT, WmRAT, and associated indicators of compromise (IOCs).