
Severity
High
Analysis Summary
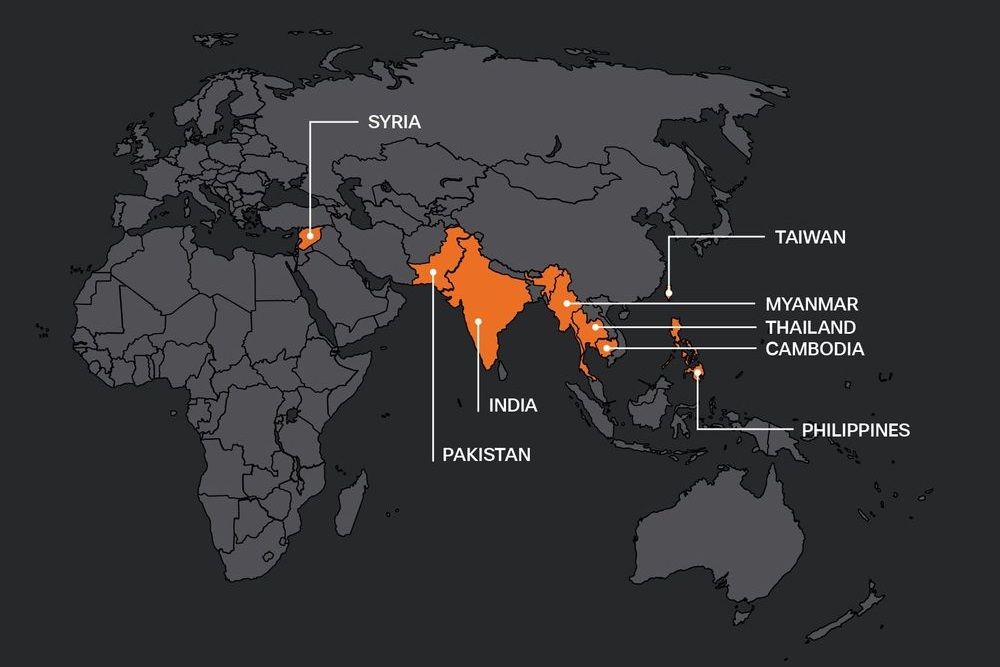
Researchers have identified UAT-11587, a China-nexus cyber-espionage activity set, while investigating a spear-phishing campaign targeting Taiwan’s academic, think-tank, and civil-society communities in March 2026. The campaign later expanded across Asia, with confirmed or probable targeting in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, Myanmar, and Syria. By July 2026, approximately 350 endpoints across eight countries were identified as compromised, primarily within government, defense, diplomatic, law-enforcement, legislative, academic, and policy organizations.
Researchers assesses UAT-11587 with high confidence as a China-nexus actor, based on multiple technical and operational indicators. These include Simplified Chinese metadata, UTC+8 timestamps, use of the China-focused rsproxy.cn Rust package mirror, and potential infrastructure overlap with another China-nexus activity cluster. Researchers assesses the campaign as an intelligence-gathering operation based on its sustained targeting of government and national-security organizations.
The campaign primarily used spear-phishing and highly tailored social engineering. Attackers spoofed trusted sender identities by exploiting differences between SMTP envelope senders and visible From headers. They also cloned Gmail’s attachment-preview interface inside malicious HTML emails, directing victims to attacker-controlled Cloudflare Pages URLs. The lures included government documents, diplomatic events, regional security topics, human-rights issues, and current geopolitical news.
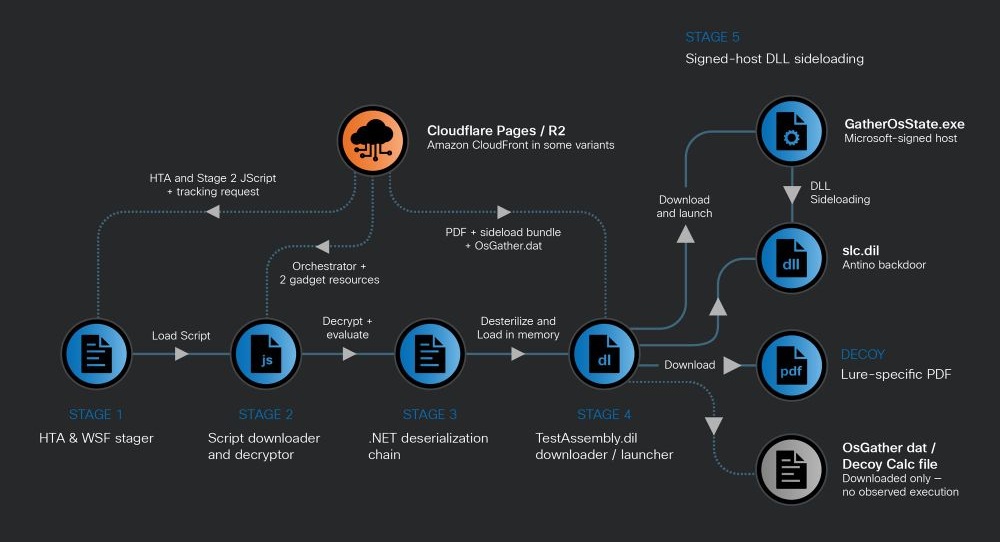
The infection chain consisted of five stages. Initial access delivered HTA or WSF stagers, followed by JavaScript downloaders that retrieved encrypted resources from Cloudflare R2 or Amazon CloudFront. RC4 decryption and .NET BinaryFormatter deserialization were then used to execute an embedded assembly. A downloader subsequently retrieved a legitimate Microsoft-signed GatherOsState.exe and malicious slc.dll, which was loaded through DLL sideloading to launch the Antino backdoor.
Antino, a Rust-based Windows backdoor, provides reconnaissance, command execution, file transfer, persistence, and shellcode execution. Its notable feature is Microsoft 365-based dead-drop C2 using Microsoft Graph, Outlook, and OneDrive. This allows communications to blend with legitimate Microsoft traffic. Antino also supports Registry Run persistence and abuses Windows Scripted Diagnostics to execute attacker-controlled PowerShell through trusted Microsoft components.
Impact
- Unauthorized Access
- Sensitive Information Theft
- Lateral Movement
Indicators of Compromise
Domain Name
- osc-cdn.com
- microsoft-flash.com
- wps-cn.com
- oisadjfoinsiduhfnoisdnfosdnoifnsoid.pages.dev
- d2nq35tel3ucuo.cloudfront.net
IP
- 103.27.110.220
MD5
- 586dd64c038ebe36c39f38d0781ce81f
- 46fa8f92dcfb524b1ee3796e1d79aa62
- ce0022848c660545b8dfb1a732957da2
- 9a2dd009889b46218f1eb0ba34bbcefa
- efdbb7015bef474b58f34281f845b1ff
- fca2d8e6bd9ed315c2324be2b3708bdc
- 3f88687ca207a17f28eadfa3764c68dc
- 132268d8a6804f2d877b96ae082ae9de
- 9ee0867162f9fe930a98d3454adf264b
- 80f759cdef77ce76d6b7cf4db20bcbe9
- df241bd3374ab72337100903f4ee161e
- bf681f76dc3b6f497d8c58e705585ae0
- b7a58329428b68f2c108a0f77f1a78fc
- d75eefe420ee327c0b81b6ed9c012114
- 764644ee9d2aaa263563619d6b1b3450
SHA-256
- 17b53ffa8e005f0e82491d3f9c0a4984c44da52e1668a855c11a137f627c5b4b
- 484ab497072ea09f12187b349f5b1c80754e4942408a009cccb20a2a3c8c6506
- 3a94910eb8022592ce030e6861359f7e980fc1b5a6ccd290cbb071d3e95ed02a
- 6a1dbbfcfe6867ac83d35012b2717084388b4a34707efd0b725466dfd0e8fa56
- b75492466462141c56d97b705f0c606faf272577631dc2822aa8d6bda53633b6
- 61a8f5add6c35f99c389012dbb2343061fd0b54611b40490b9a7f0b49d707da0
- 747b1d13bdf06956b5da5f47250fefd5284ebcf7961971732c3d348aa1a2d533
- 2f1513c822af0c6635dd3c69dc38f0b2f6e02012ea36415fff111a5d4d5fae05
- a0e91085f08956a9a7034ace73cee60cb211f5d96f02bc91a026601bde8f2221
- 09ef7c736bccfafefc44d9910d499173b88063b73b221fc0dc9e9105107e5cff
- ca14ad0344dc7216f6da29a5cbe4237d886cc5257e8c3a48fb4885a311c9b800
- b90a4e770869c28fd2140acb3ebdc50c113bb6f096b4bbdb9ac87c349c70e85e
- 9b7df409c9a89f7536d3ba7b6d43fb6dbac618c8bb52615ba34cc971ad71bbf3
- 971cb2448b5d67dcc1f5eaa10d12e77f213035ad31230dc2ac7a510610a2059d
- 5c5c060b272cd4a5c3767edc0e9478bd35b7e1756e183d0446a5491bd65519cb
SHA1
- 80e44509a78bb5723bfcc84f2235ac4a11ffd1c3
- f31806b8af4182b112e60912ae2d9944b7438603
- c8c137e12f7200a8ef02fcb73162f7e9b0422739
- 46c30044e001ec3f3715d046d39c1572ef330cb2
- 3fe4bd14923975e5e934876903f2f0260e35b754
- 5171f2578109edac2a6ee918b484d24d0bfd17c2
- 33d222dfb62374413761e0c92b3a9e5360f4134c
- bdd382bfa1b15c9c0078c7b24ebd60924537f722
- 4226027352168199e32509ee8dbddd478394372c
- 13b2809d42c3ce491008b2dca40ff86551be7897
- 5fc2fc9f15d522d5ca88d99f4bbeb45884215cd6
- e3b2bba523c035177241f6f66168e60fa6abbaaf
- 456693dd3c2ca1931306cce09a8c712aa6de9e76
- 829a3aa7be1245bc25aaf7811e1bad044dd751b1
- e8b4a1ec9ca53688fb62e29c44d631f1cbc54d9a
URL
- https://microsoft-flash.com/download/flashcenter_pp_ax_install_en.exe
- https://www.wps-cn.com/downloads/flashcenter_pp_ax_install_en.exe
- https://d2nq35tel3ucuo.cloudfront.net/9q9OlLKCm0an2ct1.js
- https://d2nq35tel3ucuo.cloudfront.net/LwqPW64Xl0ti3q7s.txt
- https://pub-abfa7742e315485a98a5fafd6dbfb68e.r2.dev/hjgzBskgGatherOsState.exe.lzj
Remediation
- Implement advanced email security controls to detect spear-phishing, spoofed sender identities, and malicious attachments.
- Block or restrict execution of HTA, WSF, and suspicious JavaScript files received through email.
- Monitor and restrict access to newly registered or suspicious Cloudflare Pages, R2, and CloudFront URLs.
- Enable endpoint detection for abnormal PowerShell, Windows Scripted Diagnostics, and DLL sideloading activity.
- Monitor Microsoft 365 Graph API, Outlook, and OneDrive activity for unusual C2-like behavior.
- Apply application allowlisting to prevent unauthorized binaries and DLLs from executing.
- Enforce least-privilege access to limit the impact of compromised accounts and endpoints.
- Conduct regular phishing-awareness training focused on highly targeted social-engineering attacks.
- Deploy and regularly update SIEM detections for associated IOCs and MITRE ATT&CK techniques.
- Isolate compromised endpoints immediately and investigate related accounts, credentials, and network activity.
- Keep operating systems, Microsoft applications, browsers, and security tools fully patched and updated.